An IoT deployment is only as secure as its weakest connection—and for cellular devices, that connection runs through the SIM. A SIM is a credential. Left unprotected, it can be removed and reused, hijacked to run up data charges, or used as a doorway into systems it was never meant to reach. The good news is that securing SIMs doesn’t require exotic tools. It requires a handful of well-understood controls, applied deliberately.
Here are the core defenses every IoT deployment should consider—what they do, when they matter, and how they fit together into a layered defense.
Why IoT SIMs Are a Target
Consumer phones get swapped, upgraded, and watched over constantly. IoT devices are the opposite: they’re deployed by the thousands, left unattended for years, and often sit in physically accessible places—a parking lot, a utility pole, a vending machine, a shipping container. That combination of accessibility and non-attended makes them attractive.
The threats are concrete. A stolen SIM can be dropped into a phone or modem to get free connectivity on your account. A compromised or malfunctioning device can burn through a data pool and inflate your bill. And a poorly isolated device can become an entry point into back-end systems. Each of these has a specific countermeasure.
IMEI Locking: Binding a SIM to Its Device
Every cellular device has an IMEI (International Mobile Equipment Identifier)—a unique hardware identifier. IMEI locking ties a SIM to a specific IMEI, so the SIM will only work in the device it was issued for.
The value is immediate. If someone pulls a, IoT SIM out of your field asset and installs it into a phone, laptop dongle, or any other device, the network sees a mismatched IMEI and refuses the connection. The stolen SIM is worthless. This single control neutralizes the most common form of IoT SIM theft—physical removal and reuse—and it’s especially valuable for unattended devices in accessible locations.
IMEI locking does require a little operational discipline: if you legitimately replace a device, you need to update the allowed IMEI for that SIM. A good management platform makes that a quick change rather than a support ticket. For example, OneSimCard IoT’s OSCAR portal allows this in just 2 clicks
Private APNs: Keeping Traffic Off the Public Internet
An APN (Access Point Name) is the gateway between the cellular network and the wider internet. By default, many SIMs use a public APN, which means your device traffic mingles with everything else and your devices are reachable—at least in principle—from the open internet.
A private APN carves out a dedicated, isolated path for your devices. Traffic travels from your SIMs into a private network segment instead of the public internet, dramatically reducing the attack surface. Your devices aren’t exposed to internet-wide scanning and probing, and you gain tighter control over exactly where their traffic can go.
Private APNs are frequently paired with a static IP address, which gives each device a fixed, known address for secure remote access, whitelisting, and reliable VPN connections. It’s worth knowing the practical constraints up front: a private APN typically requires a static IP assignment, and an account generally operates a single private APN. Planned for at the design stage, a private APN becomes the backbone of a genuinely private, controllable IoT network.
Usage Caps and Anomaly Alerts: Containing the Damage
Not every threat is an intruder. Sometimes the problem is a device that malfunctions, gets stuck in a loop, or is quietly compromised and starts behaving abnormally. The defense here is containment.
Usage caps/limits set a hard ceiling on how much data a SIM can consume in a given period (usually monthly). If a device suddenly starts transmitting more than it should, the cap suspends it automatically—turning a potential runaway bill into a contained, non-event.
Anomaly alerts/Alarms notify you when a SIM does something out of character: exceeding its normal data pattern, connecting from an unexpected location, or registering on a network it shouldn’t be on. Catching these early is often the first sign that a device has been tampered with or compromised. Together, caps and alerts mean a single bad actor—or a single faulty unit—can’t quietly drain your budget or run unchecked.
Layering the Controls
None of these measures is a complete solution on its own. Their strength is in combination:
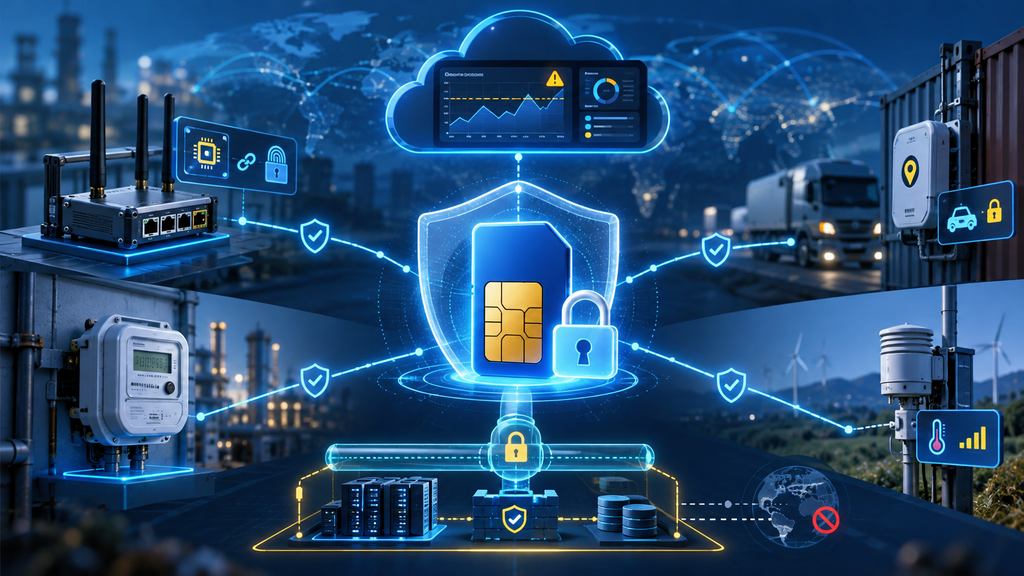
– IMEI locking stops a stolen SIM from working elsewhere.
– A private APN with a static IP keeps device traffic isolated from the public internet and under your control.
– Usage caps contain the financial damage of a runaway or hijacked device.
– Anomaly alerts give you early warning that something is wrong.
Stack them and you cover the main failure modes: physical theft, network exposure, bill shock, and undetected compromise. A SIM that’s IMEI-locked, running on a private APN with a static IP, capped at a sensible data limit, and monitored for anomalies is a genuinely hard target.
A Practical Security Checklist
When planning a deployment, work through these questions:
1. Are my SIMs IMEI-locked to their devices—especially those in accessible locations?
2. Do my devices need a private APN and static IP for isolation and secure remote access?
3. Have I set usage caps that reflect each device’s normal consumption?
4. Are anomaly and usage alerts configured so I hear about problems early?
5. Can my connectivity platform enforce all of the above from one place?
If you can answer yes to these, you’ve closed the gaps that account for the vast majority of IoT connectivity incidents.
Security Starts at the Connectivity Layer
It’s tempting to think of IoT security as purely a device-software problem—firmware, encryption, patching. All of that matters. But the connectivity layer is where some of the most practical, high-impact controls live, and it’s often the easiest place to make real gains.
At OneSimCard IoT/M2M, IoT SIMs support IMEI locking, private APNs with static IPs, and configurable usage caps and alerts through the OSCAR management platform— you can build these protections from day one and manage them across your entire fleet from a single dashboard. Secure the SIM, and you’ve secured the foundation everything else is built on.